--dangerously-skip-permissions is a command-line flag for Claude Code, Anthropic’s AI coding agent. It turns off the permission prompts, so the agent edits files and runs commands without asking you first. The name already tells you how the story can end.
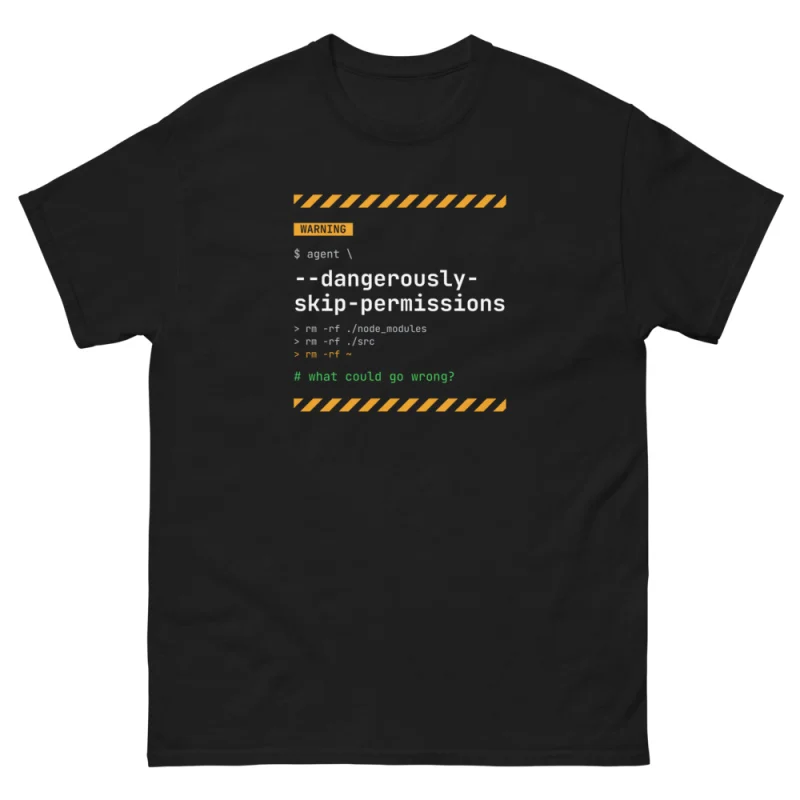
Our shirt shows the escalation in a terminal: rm -rf node_modules, then rm -rf src, then your home directory. Hazard stripes included.
What the flag does
By default, Claude Code asks before it runs a shell command or edits a file. The flag skips those questions. According to the Claude Code permission modes docs, it is equivalent to:
claude --permission-mode bypassPermissionsThe docs describe the mode plainly: it “disables permission prompts and safety checks so tool calls execute immediately”. A few protections still apply: explicit deny rules still block, and some critical deletions still prompt. On Linux and macOS, Claude Code refuses to start in this mode as root or with sudo, unless it detects a recognised sandbox.
What the docs recommend
The documentation carries two warnings about this mode:
- “Only use this mode in isolated environments like containers, VMs, or dev containers without internet access, where Claude Code cannot damage your host system.”
- “
bypassPermissionsoffers no protection against prompt injection or unintended actions.”
The second warning connects to prompt injection. If the agent reads a file or web page with hidden instructions, and nothing asks you first, those instructions can become commands. Companies can block the mode for everyone with the managed setting permissions.disableBypassPermissionsMode.
Why people use it anyway
Permission prompts are slow. An agent that stops every ten seconds to ask “may I run the tests?” is hard to leave alone. So developers reach for the flag to let a long task run unattended. Used inside a disposable container, that is a reasonable trade.
| Where you run it | Worst case |
|---|---|
| A dev container or VM with no secrets | You rebuild the container |
| Your laptop, in a project folder | Lost uncommitted work, or worse |
| Your laptop, with cloud credentials and SSH keys | Everything those keys can reach |
Why it is funny
Most dangerous options hide behind quiet names. This one puts the danger in the name, and people type it anyway, the same way they click “I accept the risks” on a certificate warning. The shirt is a confession: you know what the flag does, and you used it on a Friday afternoon.
The opposite shirt is Human in the Loop, for the person who reads every prompt before approving it.
Get the shirt
Dangerously Skip Permissions T-Shirt · 24 €
Hazard stripes for your favourite flag.
Human in the Loop T-Shirt · 24 €
The safe alternative.
Ignore All Previous Instructions T-Shirt · 24 €
The reason the docs warn you.
All shirts are unisex, S to 5XL, printed on demand in black, graphite heather and white. Check the size guide before ordering. More ideas in the Christmas gift guide for programmers.
FAQ
What does –dangerously-skip-permissions do?
It starts Claude Code in bypass permissions mode, where tool calls run without asking for approval. Deny rules and a few critical checks still apply.
Is it safe to use –dangerously-skip-permissions?
The official docs say to use it only in isolated environments, such as containers or VMs without internet access, where the agent cannot damage your host system.
Can a company disable it?
Yes. Administrators can set permissions.disableBypassPermissionsMode to "disable" in managed settings.